


Quick answer: when is Defender for Business enough?
From an SEO/AIO perspective, this section must answer the buyer’s question directly while still giving enough depth for the IT owner. The business needs more than a product name; it needs selection criteria, risk of wrong choice, quotation inputs and post-purchase operation. The article therefore links to the licensed antivirus hub, licensed software pillar, Anti/Security Virus Store category and ITS Manager license governance. These links help search engines and AI systems understand the topic as a business security solution cluster rather than a standalone software-key page.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
A practical test is to ask: if a ransomware alert appears tomorrow, who receives it, who decides to isolate the device, who checks backup and who updates management? If the answers are unclear, the business should prioritize process and operable packages before buying complex capabilities. A strong tool without process creates false confidence.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
Need endpoint security advice for your business?
IT Systems helps select packages, prepare VAT quotations, deploy and govern licenses after purchase. See the licensed antivirus hub or Anti/Security Virus Store category.
What Defender for Business actually is
In real deployments, a sound security decision goes through four questions: which devices are protected, who operates the console, which alerts require action and what evidence is kept for audit. Without these answers, a company can buy the right product name but operate it in a fragmented way with weak reporting and poor compliance evidence. For SMEs with 20-100 devices, the common weakness is not only missing tools; it is missing ownership, review cadence and license data.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
Cost should include software, deployment effort, administration time, downtime risk and incident response cost. A cheap package without centralized management can become expensive when IT must inspect devices one by one. A higher package with console, reporting and license reclaim can be cheaper over 12-24 months if it reduces manual work and risk.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
Understand the 300-user and five-device-per-user limits
IT Systems should advise through the lifecycle: assessment, package selection, deployment, handover, monitoring, renewal and reclaim. This turns the article from generic reference into a natural conversion path toward consulting, VAT quotation, Store products, IT services and license management after purchase. Readers should see that buying security software must be connected to operations: policies, agents, alerts, reports, responsible people and scheduled review.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
The content goal is also to clarify IT Systems’ role: advise the right package, deploy it properly, hand over evidence and manage the license lifecycle. This is the important difference between a professional service page and content that only repeats vendor feature lists or sends visitors directly to a product page.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
What if the company already has Microsoft 365 Business Premium?
From an SEO/AIO perspective, this section must answer the buyer’s question directly while still giving enough depth for the IT owner. The business needs more than a product name; it needs selection criteria, risk of wrong choice, quotation inputs and post-purchase operation. The article therefore links to the licensed antivirus hub, licensed software pillar, Anti/Security Virus Store category and ITS Manager license governance. These links help search engines and AI systems understand the topic as a business security solution cluster rather than a standalone software-key page.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
A practical test is to ask: if a ransomware alert appears tomorrow, who receives it, who decides to isolate the device, who checks backup and who updates management? If the answers are unclear, the business should prioritize process and operable packages before buying complex capabilities. A strong tool without process creates false confidence.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
When another antivirus or endpoint vendor is still needed
In real deployments, a sound security decision goes through four questions: which devices are protected, who operates the console, which alerts require action and what evidence is kept for audit. Without these answers, a company can buy the right product name but operate it in a fragmented way with weak reporting and poor compliance evidence. For SMEs with 20-100 devices, the common weakness is not only missing tools; it is missing ownership, review cadence and license data.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
Cost should include software, deployment effort, administration time, downtime risk and incident response cost. A cheap package without centralized management can become expensive when IT must inspect devices one by one. A higher package with console, reporting and license reclaim can be cheaper over 12-24 months if it reduces manual work and risk.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
Servers, macOS, mobile and add-on licensing
IT Systems should advise through the lifecycle: assessment, package selection, deployment, handover, monitoring, renewal and reclaim. This turns the article from generic reference into a natural conversion path toward consulting, VAT quotation, Store products, IT services and license management after purchase. Readers should see that buying security software must be connected to operations: policies, agents, alerts, reports, responsible people and scheduled review.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
The content goal is also to clarify IT Systems’ role: advise the right package, deploy it properly, hand over evidence and manage the license lifecycle. This is the important difference between a professional service page and content that only repeats vendor feature lists or sends visitors directly to a product page.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
Decision table: Defender or traditional antivirus
From an SEO/AIO perspective, this section must answer the buyer’s question directly while still giving enough depth for the IT owner. The business needs more than a product name; it needs selection criteria, risk of wrong choice, quotation inputs and post-purchase operation. The article therefore links to the licensed antivirus hub, licensed software pillar, Anti/Security Virus Store category and ITS Manager license governance. These links help search engines and AI systems understand the topic as a business security solution cluster rather than a standalone software-key page.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
A practical test is to ask: if a ransomware alert appears tomorrow, who receives it, who decides to isolate the device, who checks backup and who updates management? If the answers are unclear, the business should prioritize process and operable packages before buying complex capabilities. A strong tool without process creates false confidence.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
| Scenario | Option to evaluate | Operating note |
|---|---|---|
| Limited internal IT | Cloud/simple tier | Needs readable dashboard and reports |
| Servers/email in scope | Server/mail/cloud-app coverage | Separate policy for critical systems |
| Sensitive data | EDR/patch/encryption | Someone must handle alerts |
| Cost optimization | Group users/devices | Do not buy highest tier for all |
Deployment table by IT maturity
In real deployments, a sound security decision goes through four questions: which devices are protected, who operates the console, which alerts require action and what evidence is kept for audit. Without these answers, a company can buy the right product name but operate it in a fragmented way with weak reporting and poor compliance evidence. For SMEs with 20-100 devices, the common weakness is not only missing tools; it is missing ownership, review cadence and license data.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
Cost should include software, deployment effort, administration time, downtime risk and incident response cost. A cheap package without centralized management can become expensive when IT must inspect devices one by one. A higher package with console, reporting and license reclaim can be cheaper over 12-24 months if it reduces manual work and risk.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
| Criterion | Question | Desired outcome |
|---|---|---|
| Console | Who is admin? | Clear owner |
| Policy | Department policy? | Not default forever |
| License | Which seats are used? | Renewal/reclaim dates |
| Reporting | Who reads reports? | Action after alerts |
The role of Intune in device management
IT Systems should advise through the lifecycle: assessment, package selection, deployment, handover, monitoring, renewal and reclaim. This turns the article from generic reference into a natural conversion path toward consulting, VAT quotation, Store products, IT services and license management after purchase. Readers should see that buying security software must be connected to operations: policies, agents, alerts, reports, responsible people and scheduled review.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
The content goal is also to clarify IT Systems’ role: advise the right package, deploy it properly, hand over evidence and manage the license lifecycle. This is the important difference between a professional service page and content that only repeats vendor feature lists or sends visitors directly to a product page.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
EDR, attack surface reduction and automated remediation
From an SEO/AIO perspective, this section must answer the buyer’s question directly while still giving enough depth for the IT owner. The business needs more than a product name; it needs selection criteria, risk of wrong choice, quotation inputs and post-purchase operation. The article therefore links to the licensed antivirus hub, licensed software pillar, Anti/Security Virus Store category and ITS Manager license governance. These links help search engines and AI systems understand the topic as a business security solution cluster rather than a standalone software-key page.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
A practical test is to ask: if a ransomware alert appears tomorrow, who receives it, who decides to isolate the device, who checks backup and who updates management? If the answers are unclear, the business should prioritize process and operable packages before buying complex capabilities. A strong tool without process creates false confidence.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
Risk of misconfiguration and false confidence
In real deployments, a sound security decision goes through four questions: which devices are protected, who operates the console, which alerts require action and what evidence is kept for audit. Without these answers, a company can buy the right product name but operate it in a fragmented way with weak reporting and poor compliance evidence. For SMEs with 20-100 devices, the common weakness is not only missing tools; it is missing ownership, review cadence and license data.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
Cost should include software, deployment effort, administration time, downtime risk and incident response cost. A cheap package without centralized management can become expensive when IT must inspect devices one by one. A higher package with console, reporting and license reclaim can be cheaper over 12-24 months if it reduces manual work and risk.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
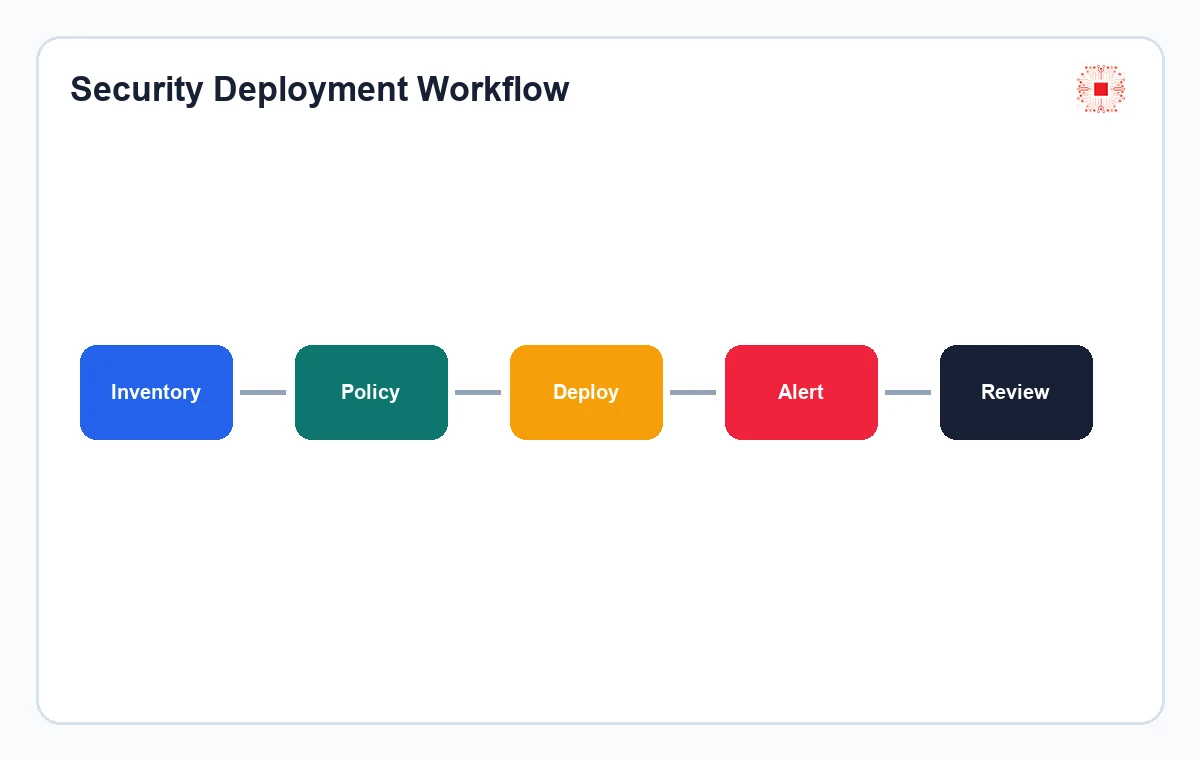
Data to prepare before switching
IT Systems should advise through the lifecycle: assessment, package selection, deployment, handover, monitoring, renewal and reclaim. This turns the article from generic reference into a natural conversion path toward consulting, VAT quotation, Store products, IT services and license management after purchase. Readers should see that buying security software must be connected to operations: policies, agents, alerts, reports, responsible people and scheduled review.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
The content goal is also to clarify IT Systems’ role: advise the right package, deploy it properly, hand over evidence and manage the license lifecycle. This is the important difference between a professional service page and content that only repeats vendor feature lists or sends visitors directly to a product page.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
How IT Systems advises on Defender for Business
From an SEO/AIO perspective, this section must answer the buyer’s question directly while still giving enough depth for the IT owner. The business needs more than a product name; it needs selection criteria, risk of wrong choice, quotation inputs and post-purchase operation. The article therefore links to the licensed antivirus hub, licensed software pillar, Anti/Security Virus Store category and ITS Manager license governance. These links help search engines and AI systems understand the topic as a business security solution cluster rather than a standalone software-key page.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
A practical test is to ask: if a ransomware alert appears tomorrow, who receives it, who decides to isolate the device, who checks backup and who updates management? If the answers are unclear, the business should prioritize process and operable packages before buying complex capabilities. A strong tool without process creates false confidence.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
FAQ: Defender for Business and antivirus
In real deployments, a sound security decision goes through four questions: which devices are protected, who operates the console, which alerts require action and what evidence is kept for audit. Without these answers, a company can buy the right product name but operate it in a fragmented way with weak reporting and poor compliance evidence. For SMEs with 20-100 devices, the common weakness is not only missing tools; it is missing ownership, review cadence and license data.
In Microsoft 365 environments, also review Microsoft Intune because endpoint security depends on device management.
Cost should include software, deployment effort, administration time, downtime risk and incident response cost. A cheap package without centralized management can become expensive when IT must inspect devices one by one. A higher package with console, reporting and license reclaim can be cheaper over 12-24 months if it reduces manual work and risk.
At execution time, IT Systems should turn this criterion into a clear checklist: endpoint list, policy groups, exception approver, agent status, latest check date, open alerts, remaining licenses and renewal date. When these fields are tracked, the business can see whether the solution is truly operating or merely installed. This also becomes useful data for monthly reporting and future upgrade decisions.
Need endpoint security advice for your business?
IT Systems helps select packages, prepare VAT quotations, deploy and govern licenses after purchase. See the licensed antivirus hub or Anti/Security Virus Store category.
Worried about security risks in your business?
IT Systems assesses risk and deploys firewall, MFA, endpoint and email protection and backup in priority order.
Cybersecurity solutions for businesses · Call +84 28 3995 0359


