Quick answer: security risks of working from home (WFH) and how to prevent them. Working from home is convenient but increases security risk. Common risks: (1) insecure home or public Wi-Fi; (2) poorly protected personal devices (unpatched, no antivirus); (3) more phishing; (4) accessing sensitive data over unencrypted connections; (5) sharing computers with family, and lost or stolen devices. Prevention: (1) use a VPN to access company resources; (2) enable MFA and strong passwords; (3) keep systems updated and use antivirus/firewall; (4) secure home Wi-Fi (WPA2/WPA3, change the router password); (5) be wary of unfamiliar emails and links; (6) lock your screen and encrypt drives (BitLocker); (7) don’t use work computers for risky personal activities. Businesses should have a WFH policy and training.
Working online from home reduced the risk of spreading Covid-19, but it also created certain risks.
As the pandemic developed, many Vietnamese businesses had staff work remotely, or in rotating shifts, to fight the outbreak while keeping work going. This reduced infection risk but introduced new security risks.
To help businesses improve information security, experts from Vietnam Cyberspace Security Technology (VSEC) shared common security risks in remote working and how to prevent them.
Accessing sensitive data over insecure Wi-Fi
Remote workers often connect through home or public Wi-Fi access points (cafés, restaurants, etc.). These are usually configured loosely, with default or publicly known admin passwords, making intrusion or spoofing easy, especially on public Wi-Fi.

On public wireless networks, VSEC recommends:
- Use a VPN (virtual private network) to encrypt your traffic when connecting to the internet.
- Configure the computer’s firewall to block unauthorised access.
- Install antivirus and anti-malware software and keep it updated.
Because remote staff access company resources, businesses shouldn’t use unencrypted username/password authentication. Staff also shouldn’t work with critical company data on public wireless networks.
Lack of face-to-face contact
With remote work, online tools (email, chat and video apps) became the main way to communicate. This makes scams easier for attackers who take over systems or steal the accounts of key staff (often executives, finance or HR).

Common scams include spoofed emails in a colleague’s name, requests for personal information, or tricking users into downloading malware or infected documents. Attackers also exploit public interest in topical events such as the pandemic to spread malware.
When communicating through online tools:
- Never share personal or financial information via email or messages.
- Don’t click links or download documents unless you’re completely sure.
- If in doubt, verify through another trusted channel.
Using personal devices for work
In the office, staff use company computers with up-to-date operating systems, antivirus and properly configured firewalls to minimise data loss. Personal home computers are often not updated regularly and have weak or no firewalls, making them easy targets.
Data can also leak when personal computers are shared with others. VSEC recommends limiting the use of personal devices for work. Where unavoidable, make sure devices have the latest operating system, antivirus, firewall and security patches.
Ignoring basic physical security in public
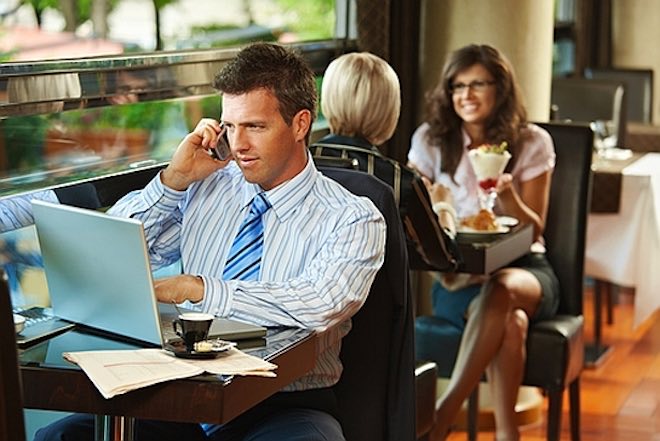
Beware of people looking at your screen or overhearing loud calls.
Even with network security in place, physical gaps can expose sensitive company information — staff talking loudly on the phone in public, leaving laptop screens visible, or leaving devices unattended.
VSEC recommends physical security measures for sensitive information and making sure staff follow even the most basic precautions.
Handling sensitive information incorrectly
It’s hard to ensure staff follow security rules remotely — for example, unused mobile devices aren’t controlled, or confidential documents are “deleted” but remain in the recycle bin.
VSEC stresses applying security policies and training thoroughly, and disposing of outdated devices properly (for example, upgrading them or physically destroying hard drives).
Losing data storage devices
Remote staff may work at home or in public places, and moving around increases the risk of loss or theft compared with a secure office. Whether accidental or deliberate, a device in outside hands means its data could be exposed.
VSEC advises not leaving devices in uncontrolled places and, when important content must be taken out, storing it on encrypted, secure USB drives.
Source: Dan Viet newspaper (danviet.vn), citing VSEC experts.
For secure remote-work setup (VPN, MFA, device management) for your business, contact IT Systems at hotline 028.3995.03.59 or contact@itsystems.com.vn.
Unstable office network that needs redesigning?
IT Systems surveys, designs and deploys LAN, Wi-Fi, firewall and VPN for offices and branches, with full documentation.